
Regulated organisations
Evidence you can hand to an auditor.
For every product, what is recorded and what never is, written down. Exports that carry their own fingerprint. Data classes, retention and deletion on one page. No badge we cannot show you the evidence for.
Custody
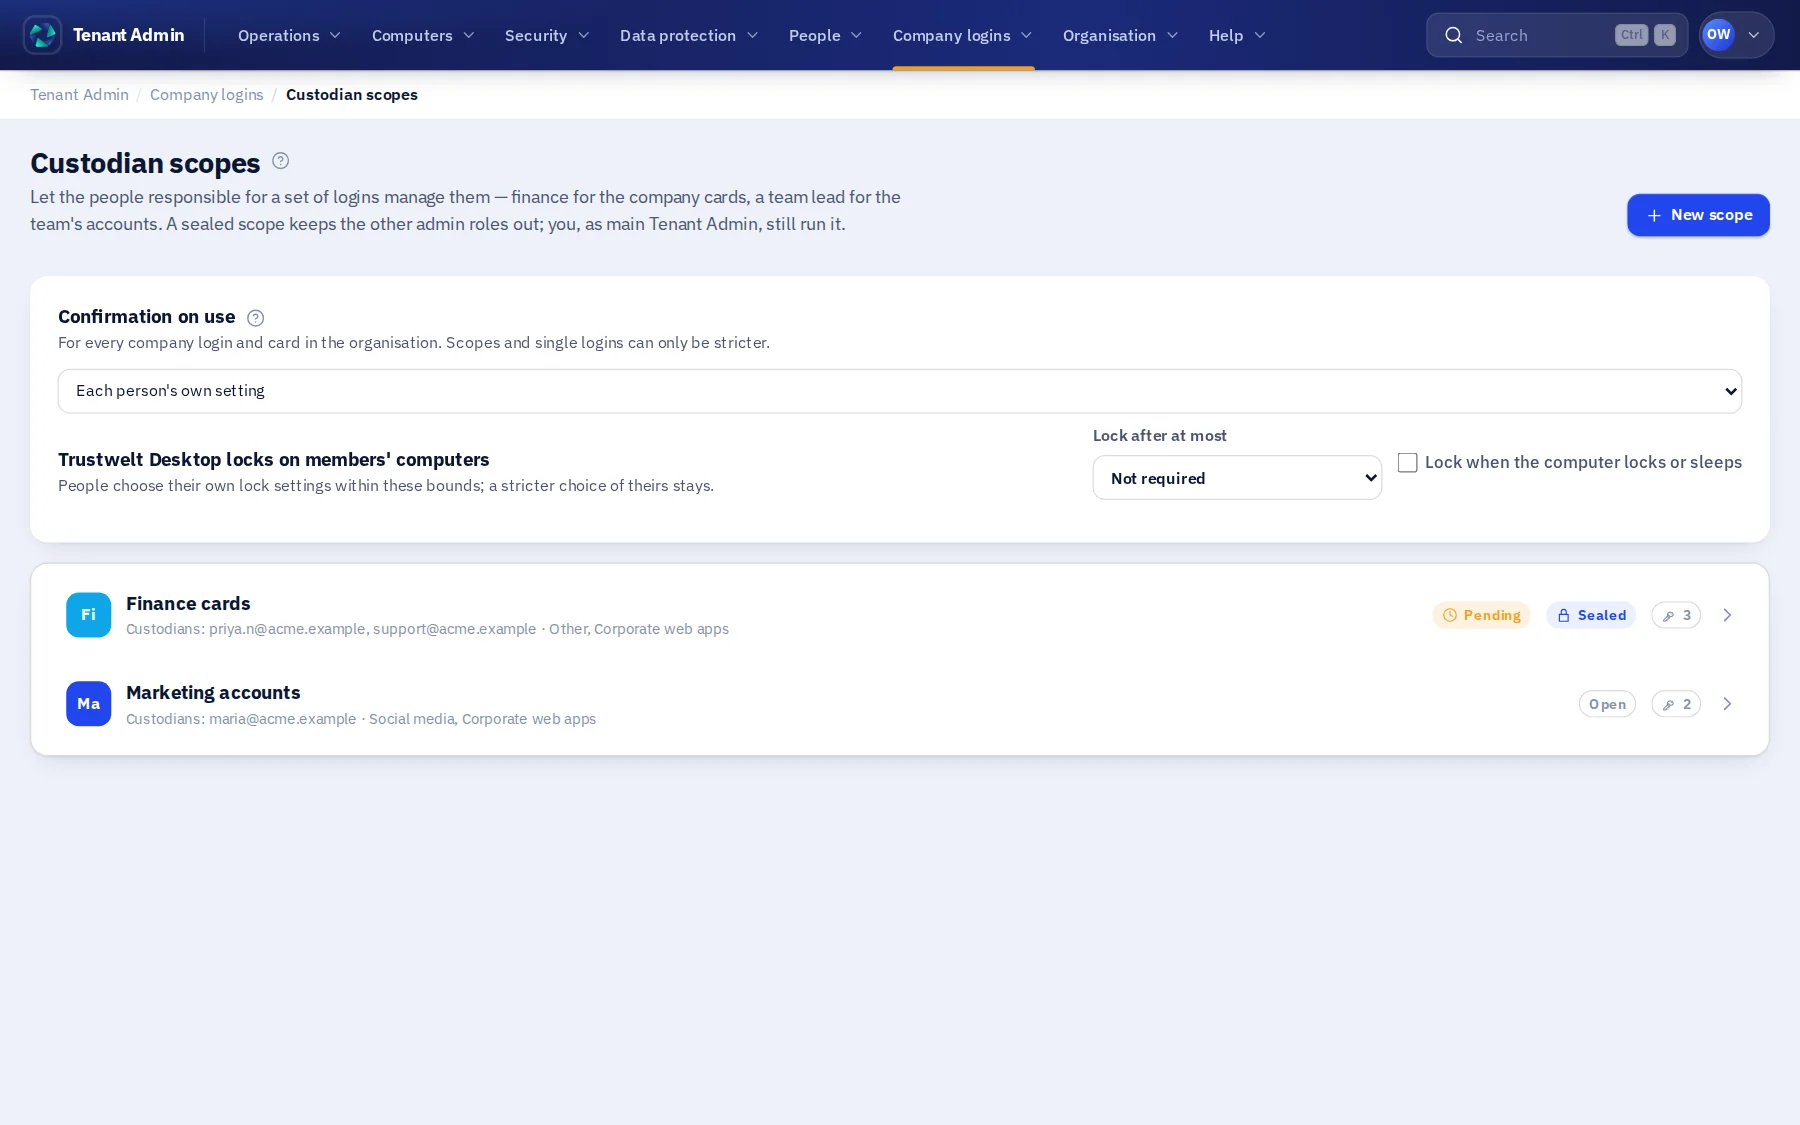
Sensitive logins and cards sealed from organisation-wide admins.
- Custodian scopes: the people who own an area run it; an ordinary admin sees its name and a count, not the items.
- Changes to a scope's custodians take two people.
- On Enterprise, an organisation-held recovery key, kept offline as a code.
- Every use of a company login or card is in the usage audit, with the amount for a card.
Evidence
What you can show.
- Recorded and neverEvery product page lists what Trustwelt records and what it never does.
- Content checksDLP and AI Security check text on the computer; Trustwelt receives the kind of finding and a count, not the text.
- ExportsCSV and PDF with the time to the second, a SHA-256 fingerprint and the exporter; each export is recorded.
- AuditPrivileged changes and refused attempts in a hash-chained record.
- WhereData stored in the EU; Trustwelt Secure MailGW checks mail at its gateway in the United Kingdom.
- Personal data of your peopleThe organisation sees counts of personal activity at most.
Walk your assessor through it.
We map your control requirements onto what Trustwelt records, and say plainly where each one is answered.