
Enterprise
Administration, evidence and custody for large organisations.
Delegated administration with exceptions per person and group, reports that stand as evidence under your own logo, a signed stream to your SIEM, and company server keys your people use without holding them.
Administration
Admin areas with exactly the authority you give them.
- A main Tenant Admin and delegated admins for HR, IT, finance or your own areas.
- Every setting can carry an exception for a person or a group, with an end date, and the change is in the audit with its before and after.
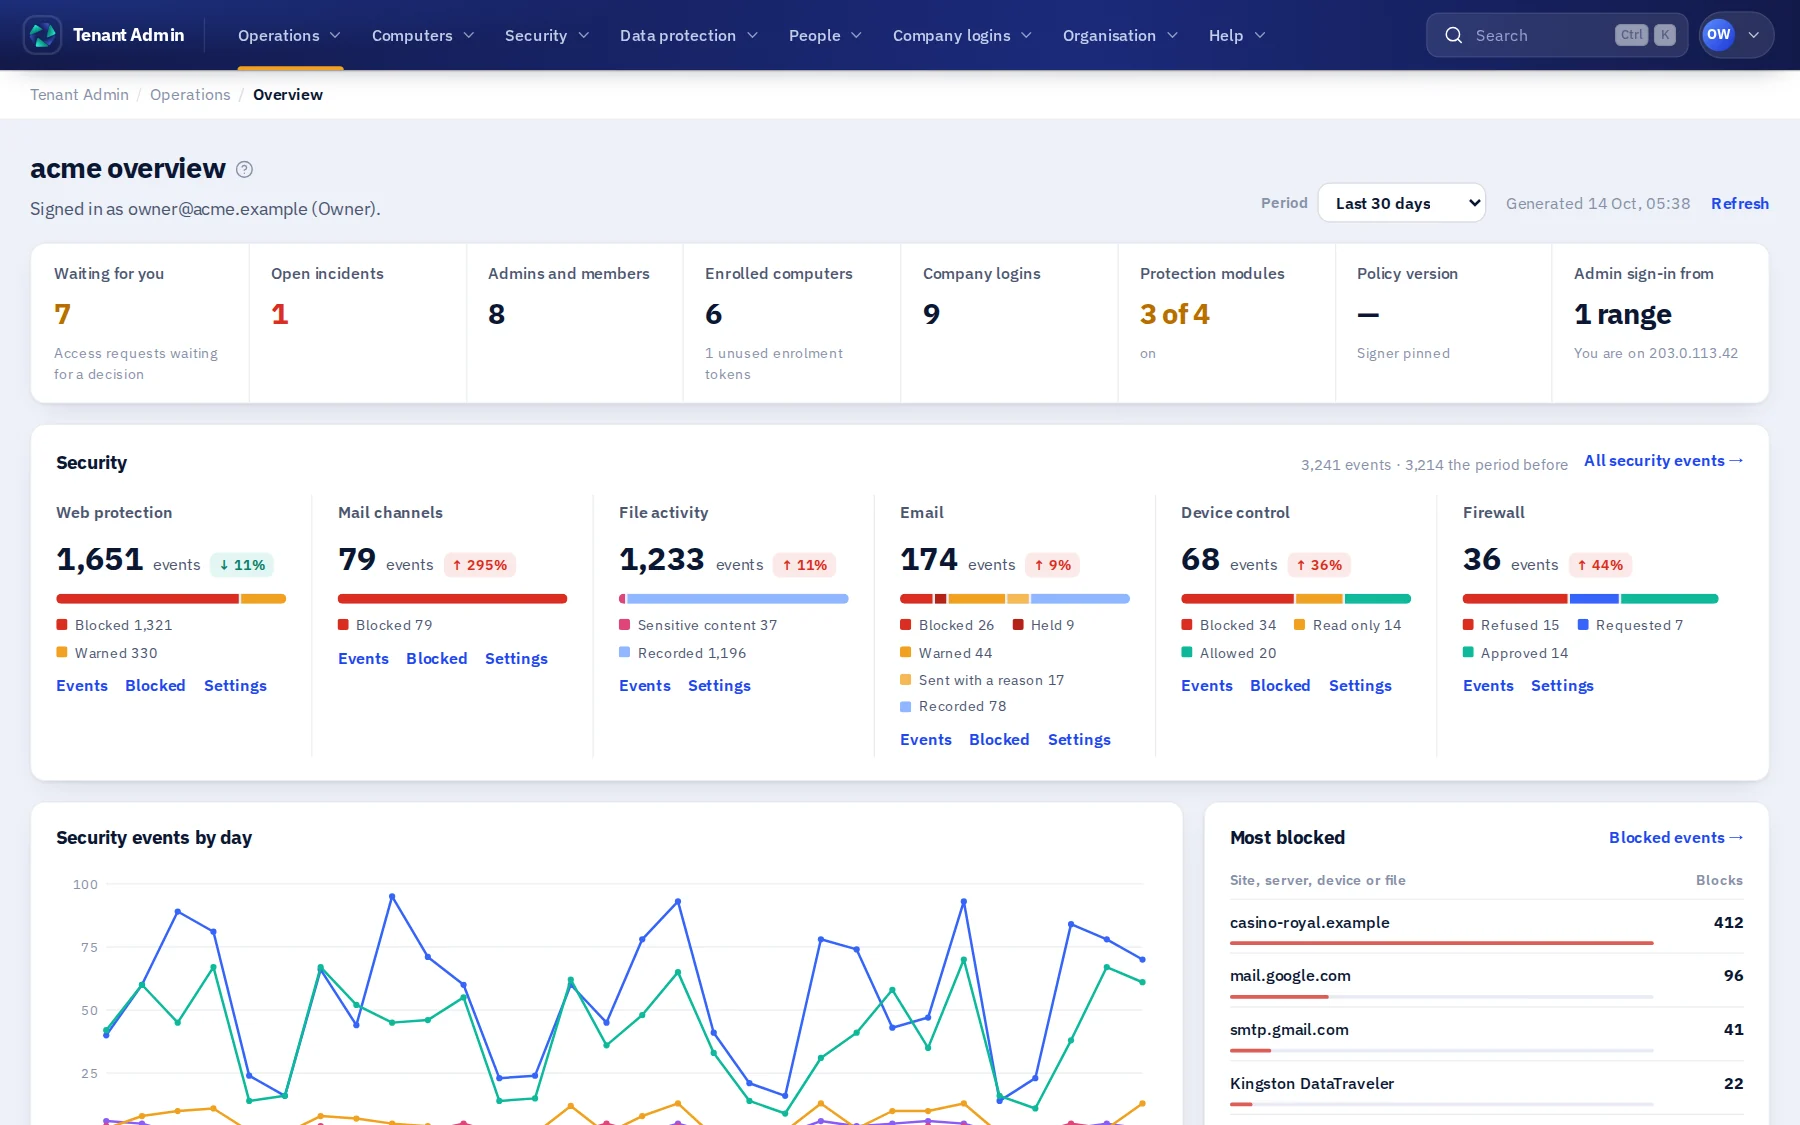
- Managed computers that ask nothing of the person: always on, web rules in every application, an e-mail when one stops reporting.
- Registered, signed remediation instead of remote shells.
- Unlimited computers.
Evidence
Reports you can hand on.
PDF and CSV, as evidence
Every export carries the time to the second in UTC, a SHA-256 fingerprint and who exported it; the export itself is recorded. Enterprise puts your own logo and heading on it.
A signed stream to your SIEM
Security events reach your endpoint in batches signed with HMAC-SHA256, every five minutes; the position moves on only when your endpoint accepts a batch.
An audit nobody edits
Every privileged change and every refused attempt is written to a hash-chained record.
Keys
Keys your people use without holding them.
- Company serversSSH keys for company servers are made or uploaded in Tenant Admin; people and allowed AI agents use them through the vault on their computer, which never shows them.
- AI agents in engineeringClaude Code, Codex CLI, GitHub Copilot, Cursor and Gemini CLI run behind Trustwelt's gateway on the computer: each tool call decided by your rules, model calls through your providers only with the key put in from the vault, workspaces and connections confined, every session on record.
- Company logins and cardsFilled under a one-time permission, never shown on screen, in a clipboard or in an export.
- RecoveryOn Enterprise the organisation holds its own recovery key for custodian scopes, kept offline as a code.
- Personal vaultsEach person's vault is encrypted on their computer with a key Trustwelt never holds.
Deployment
Trustwelt runs as a service.
The platform runs at Trustwelt and an organisation's data is stored in the EU; the content checks of DLP and AI Security run on the computer itself. If your organisation needs part of Trustwelt inside its own network, we talk it through with your architects.